Access Control in Activate
All Activate objects and parameters have Access Control Lists (ACLs) that govern access to the object. This works similarly to the Windows File System or Active Directory.
Standard Rights
All objects support the following standard rights:
- Create — Permission to create child objects.
- Read — Ability to read child objects and parameters.
- Write — Ability to modify the object's properties and parameters.
- Delete — Permission to delete the object.
Access Control Lists (ACLs)
Each ACL contains a list of Access Control Entries (ACEs). An ACE can either Allow or Deny access.
Access Deny ACEs are very powerful and override all other permissions. Use with caution.
Each ACE defines:
- Trustee — The role to which the security applies. (Note: users cannot be granted access directly — only Activate roles can be assigned.)
- ACE Type — Either Allow or Deny.
- Rights — The specific rights granted or denied to the trustee.
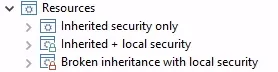
In Activate Studio, padlock icons indicate the state of inherited security on objects:
- No padlock — Inherited security only.
- Green padlock — Inherited + local security.
- Red padlock — Broken inheritance with local security.
Extended Security Rights
Some Activate objects support extended security rights, which are specific to the object type and control different aspects of its behaviour.
Common extended rights include:
- VIEW — Permission to view instances of the object (e.g., viewing service instances on a Service object).
- USE — Permission to use the object (e.g., for Services, this allows users to use the service). On Tasks, this right is called EXECUTE.
- CREATE INSTANCE — Permission to create an instance of the object (e.g., creating a service instance).
- UPDATE INSTANCE — Permission to update an instance of the object.
- DELETE INSTANCE — Permission to delete an instance of the object.
Rights Matrix
Object | Read | Write | Create | Delete | Use | View | Create I | Update I | Delete I | Approvers |
|---|---|---|---|---|---|---|---|---|---|---|
Base | ✅ | ✅ | ✅ | ✅ | | | | | | |
ProvisioningDirectory Entry | | | | | | | | | | |
User Directory Entry | | | | | | | | | | |
Role | ✅ | ✅ | ✅ | ✅ | USE | VIEW | ADDUSER | | | |
Service | ✅ | ✅ | ✅ | ✅ | USE | VIEW | ADD | UPDI | DELI | |
Asset | ✅ | ✅ | ✅ | ✅ | USE | VIEW | | | | |
Task | ✅ | ✅ | ✅ | ✅ | EXECUTE | VIEW | | | | |
FolderResource | ✅ | ✅ | ✅ | ✅ | USE | VIEW | ADDUSER | | | ADDAPPROVER |
WSSResource | ✅ | ✅ | ✅ | ✅ | USE | VIEW | ADDUSER | | | ADDAPPROVER |
DL | ✅ | ✅ | ✅ | ✅ | USE | VIEW | ADDUSER | | | ADDAPPROVER |
SecurityGroup | ✅ | ✅ | ✅ | ✅ | USE | VIEW | ADDUSER | | | ADDAPPROVER |